Are you keeping up with cybersecurity? The new NIS 2 Directive introduces new requirements and will affect many companies across Europe.
Are you keeping up with cybersecurity? Is your company well protected against hacker attacks? The new NIS 2 Directive introduces new requirements and measures in this area and will affect many companies across Europe. It has been adopted since 2022 and is currently being transposed into German and Austrian law.
Who is affected?
This is probably one of the questions you’re now asking for your company.
The Directive applies to public or private entities in various sectors. It’s already clear that more sectors (from 8 to 18) and more companies per sector will be affected than under the current NIS Directive.

Sectors of high criticality (+3) h3 >

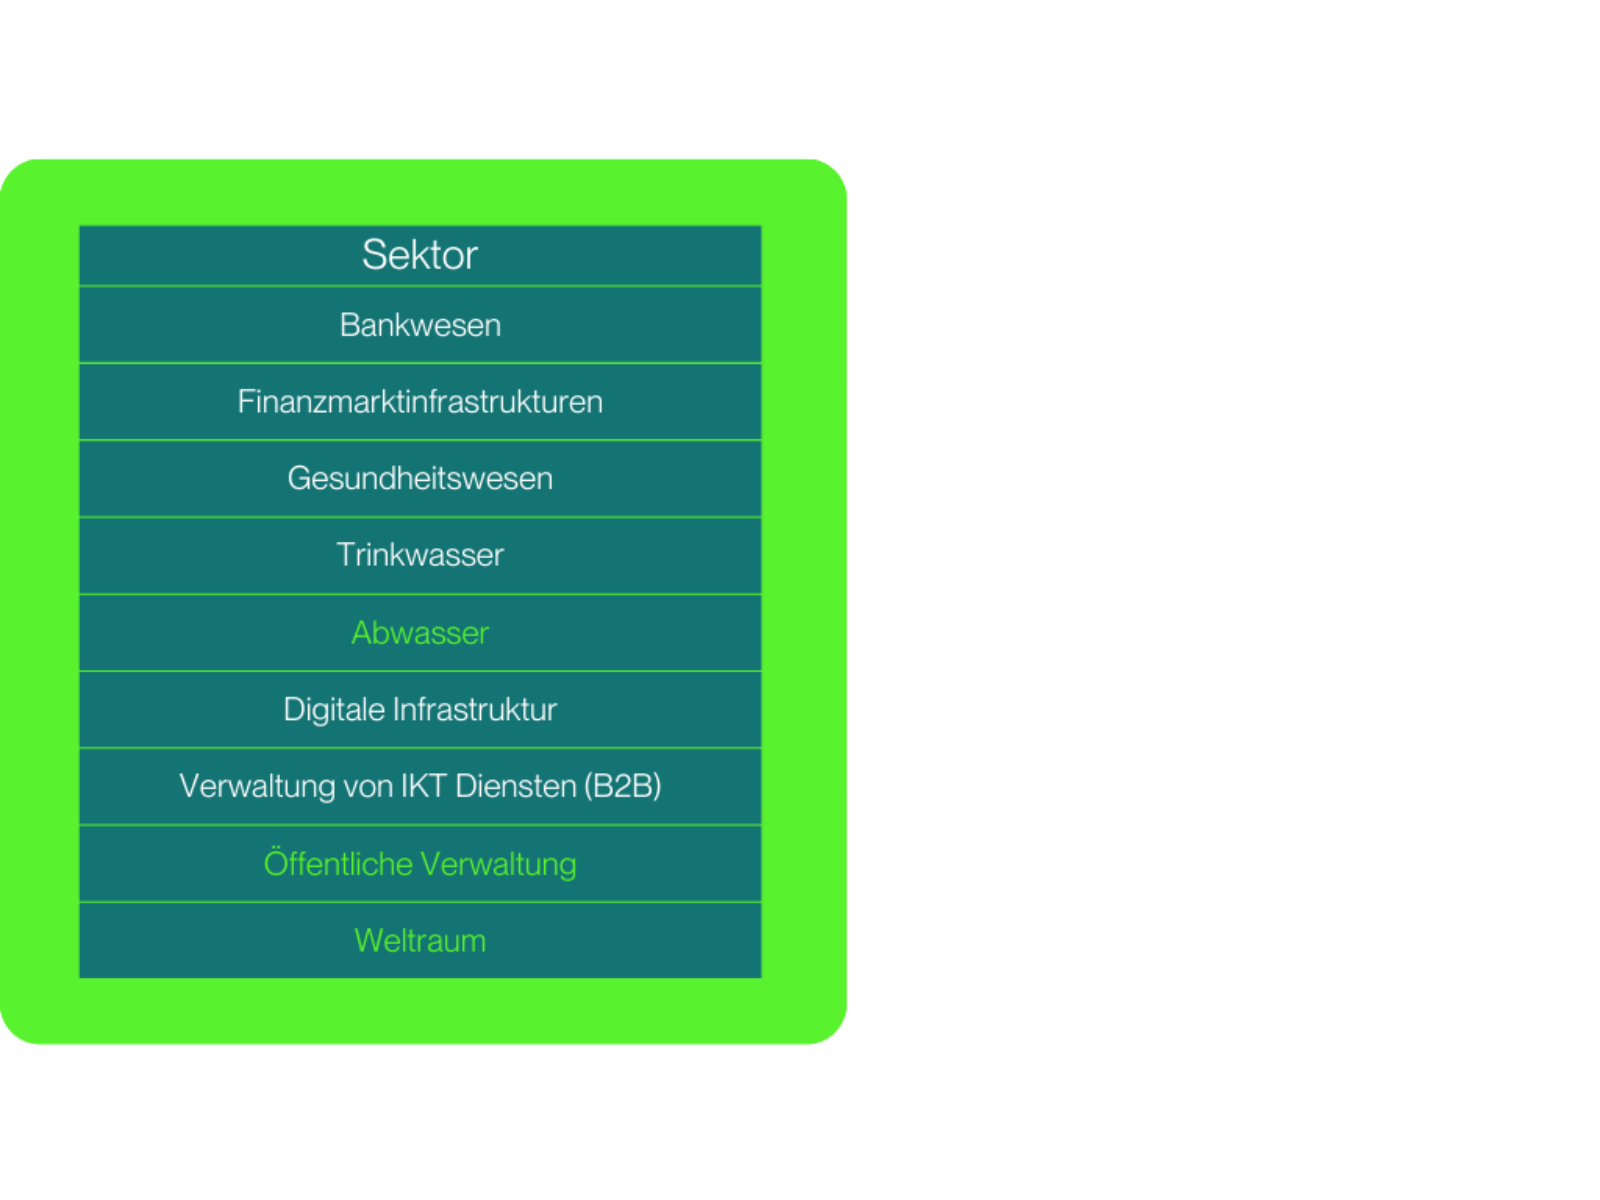
Other critical sectors (+6) h3 >


The threshold for affected companies (Art. 1(1) NIS 2 Directive) is
Medium-sized companies
- 50–250 employees
- Between €10 and €50 million in revenue
- Less than €43 million in total assets
Large companies
- More than 250 employees
- More than €50 million in revenue
- More than €43 million in total assets
The NIS 2 Directive includes expanded mandatory security measures with specific minimum requirements for, among other things, concepts for risk analysis for information systems and information system security, crisis management and BCM, incident management, supply chain security, cyber hygiene, and much more.
Have you already established a process for reporting cybersecurity incidents in your risk management system? Have you already developed concepts for risk management and for the security of network and information systems?
Great! Then you’re already on a very good path. If these topics are still open for you and your company falls within the affected sectors and thresholds, our recommendation is to start working on implementing NIS 2 compliance as soon as possible.
Depending on which systems and processes are already in place, the project duration for implementing NIS 2 takes several months.
In the CRISAM® GRC platform, implementing the NIS 2 Directive is easy. Integrate NIS 2 into your existing ISMS and also use dashboards and tailored reports to generate exactly the evaluation and documentation capabilities required at the push of a button.
From a business perspective, implementing the NIS 2 Directive should not be seen as a “necessary evil”, but rather as an opportunity to send a signal. You will meet the highest European standards in cybersecurity and be as well prepared as possible for hacker attacks.
Business processes are better protected, and the risk of data loss and operational outages is significantly minimized.
You also protect your company from substantial fines, which can range from €7 to €10 million or 1.4–2% of total annual turnover (depending on which category your entity falls into).
No risk – just get in touch with us!
Would you like more information? Do you have questions about implementing the new NIS 2 Directive?
So you can prepare your company, we have implemented the EU Directive in a catalog (NIS 2) as a module (NIS 2 EU). These 35 control objectives make implementing the new Directive significantly easier.
Feel free to get in touch with us.
We support you in this process with CRISAM® GRC!

Would you like to get to know us?