CRISAM® GRC at Stadtwerke Bonn | Case Study
Essen, September 2026 – At the 2nd IT Security Day for Network Partners in Essen, CRISAM® and Stadtwerke Bonn demonstrated how integrated information security and risk management can be built on a shared data foundation. The case study illustrated the journey from modelling and business impact analysis through to risk analysis and the prioritisation of specific measures.
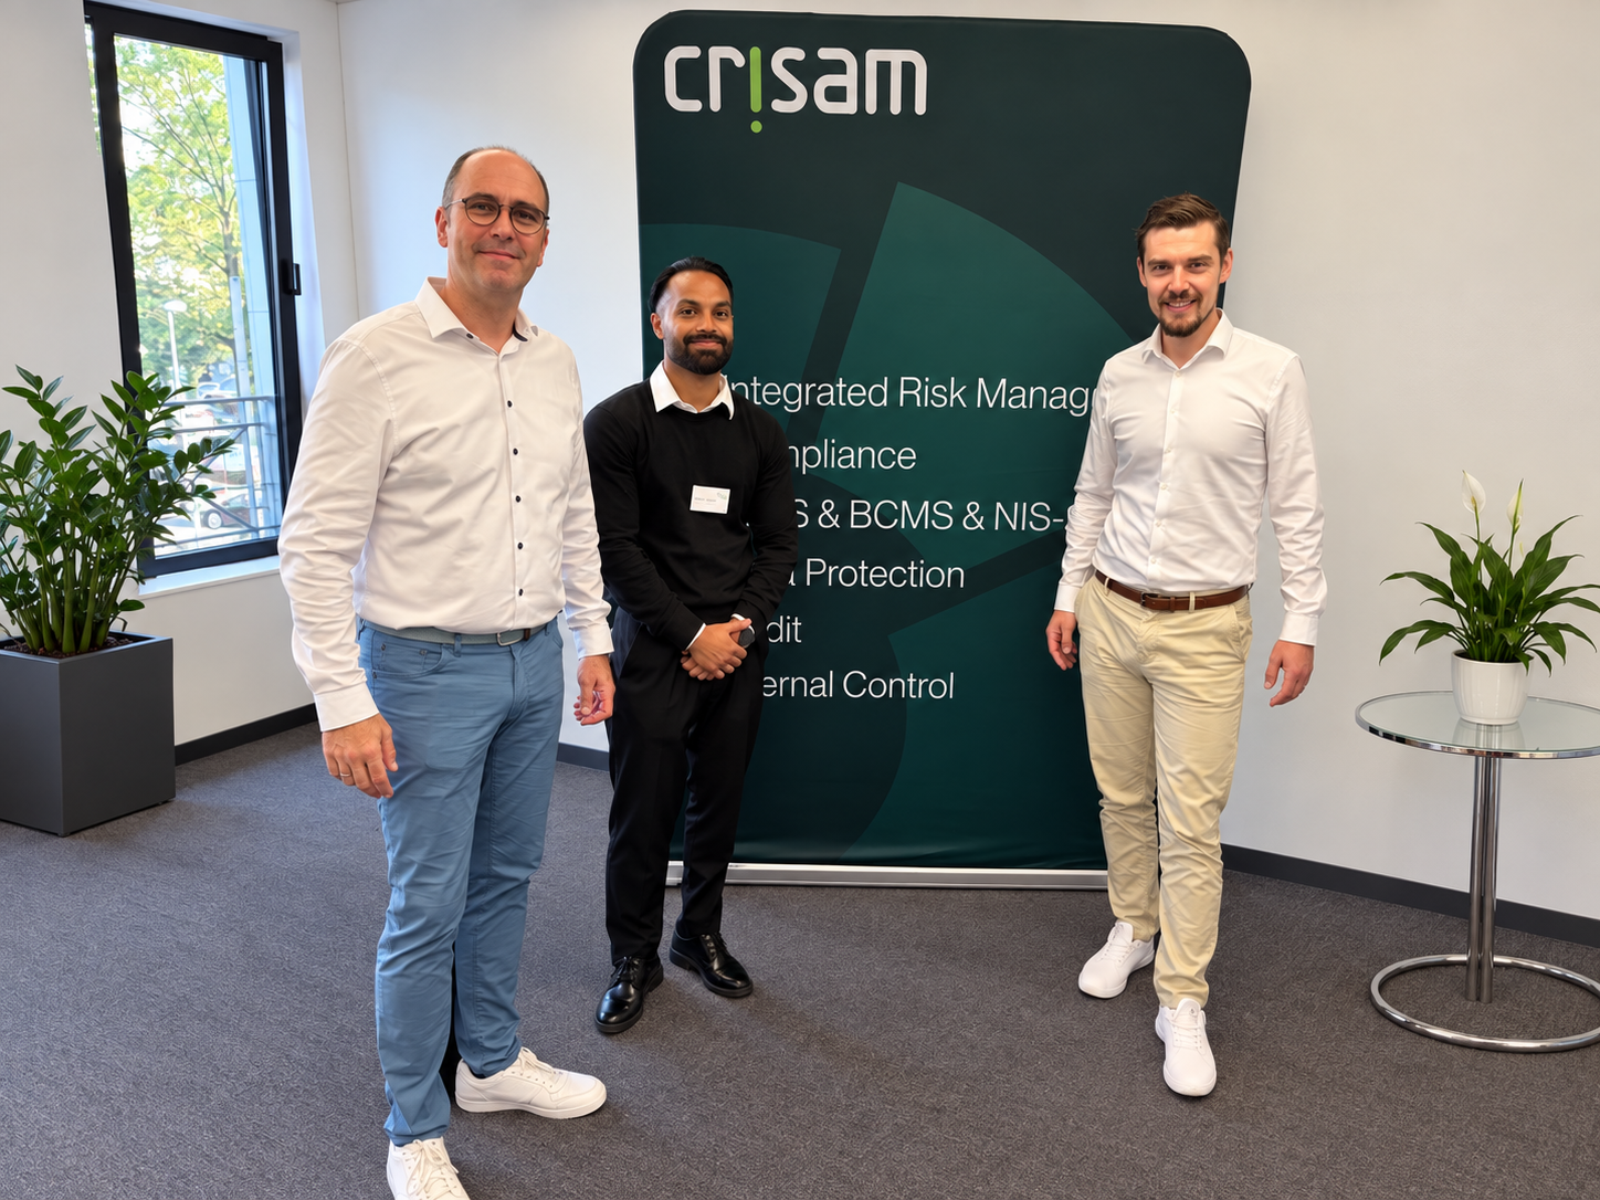
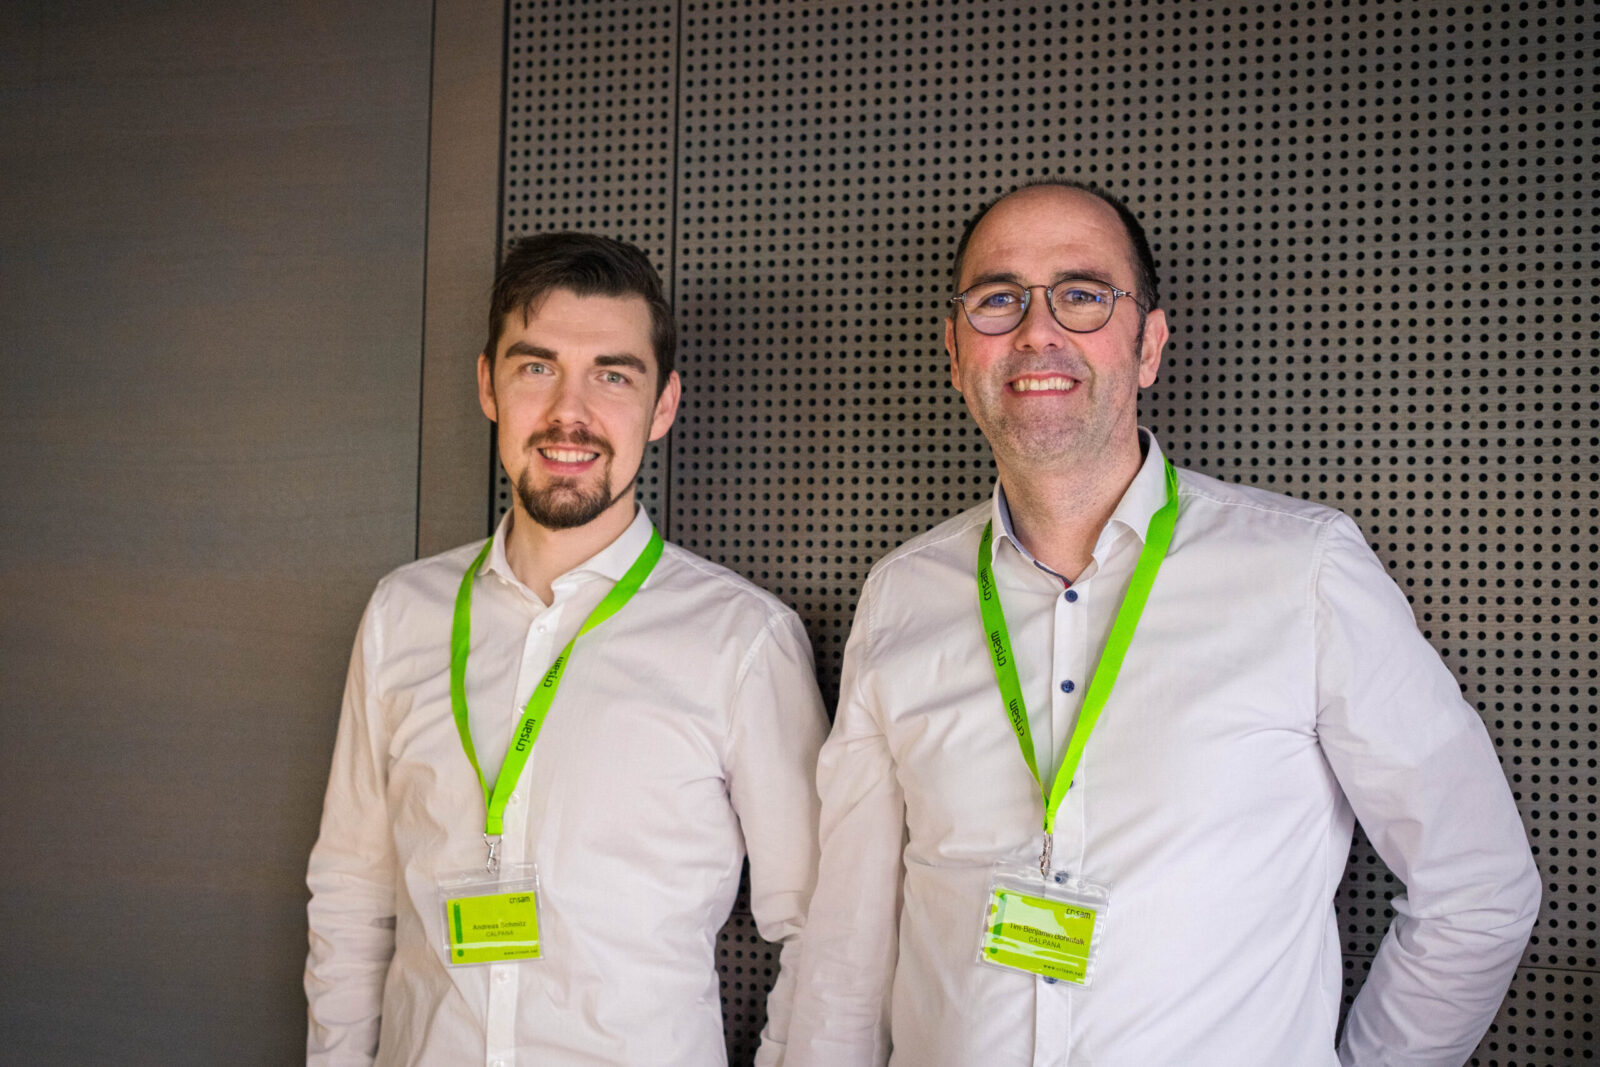
On 22 September 2026, experts came together at the 2nd IT Security Day for Network Partners in Essen to discuss current requirements in information security, governance and regulation. Together with Stadtwerke Bonn, CRISAM® demonstrated how governance, risk and compliance can be integrated with information security and business continuity on a single platform. Tim-Benjamin Bohmfalk presented the platform, while Rita Bohlmann provided insights into its practical implementation.
Today, organisations must meet numerous requirements in parallel – from IDW PS 340 n.F. and NIS2 to the AI Act, ISO standards and increasing documentation obligations. At the same time, these requirements often meet established processes based on Excel spreadsheets, email chains and isolated solutions that do not adequately connect data, responsibilities and evidence.
Particularly in the run-up to audits and management meetings, this results in considerable coordination effort. Information has to be consolidated manually, evidence is stored across different locations, and status reports require significant effort to prepare. This makes it more difficult to maintain a consistent view of risk and delays decision-making.
CRISAM® GRC therefore follows an integrated platform approach. Risk management, the internal control system, audit management, ISMS and BCMS, data protection, ESG and CSRD, compliance, and tax compliance all use the same data foundation. Organisations can start with a single module and add further disciplines over time without having to introduce another separate system with its own data repository.
Configurable workflows map responsibilities and multi-stage approval processes. Deadlines, reminders and escalations are managed directly within the process. Every change remains traceable through version control and an audit trail. Dashboards, digital approvals, and exports to Office or PDF support the preparation of information for management, executive boards and supervisory bodies.
Stadtwerke Bonn employs around 2,800 people. Its responsibilities span energy and water supply, waste management, mobility and public transport. This diversity makes the interdependencies between critical services, IT processes, core services and infrastructure particularly important. In Essen, Rita Bohlmann explained how CRISAM® provides a structured representation of these interdependencies as a basis for further analysis.
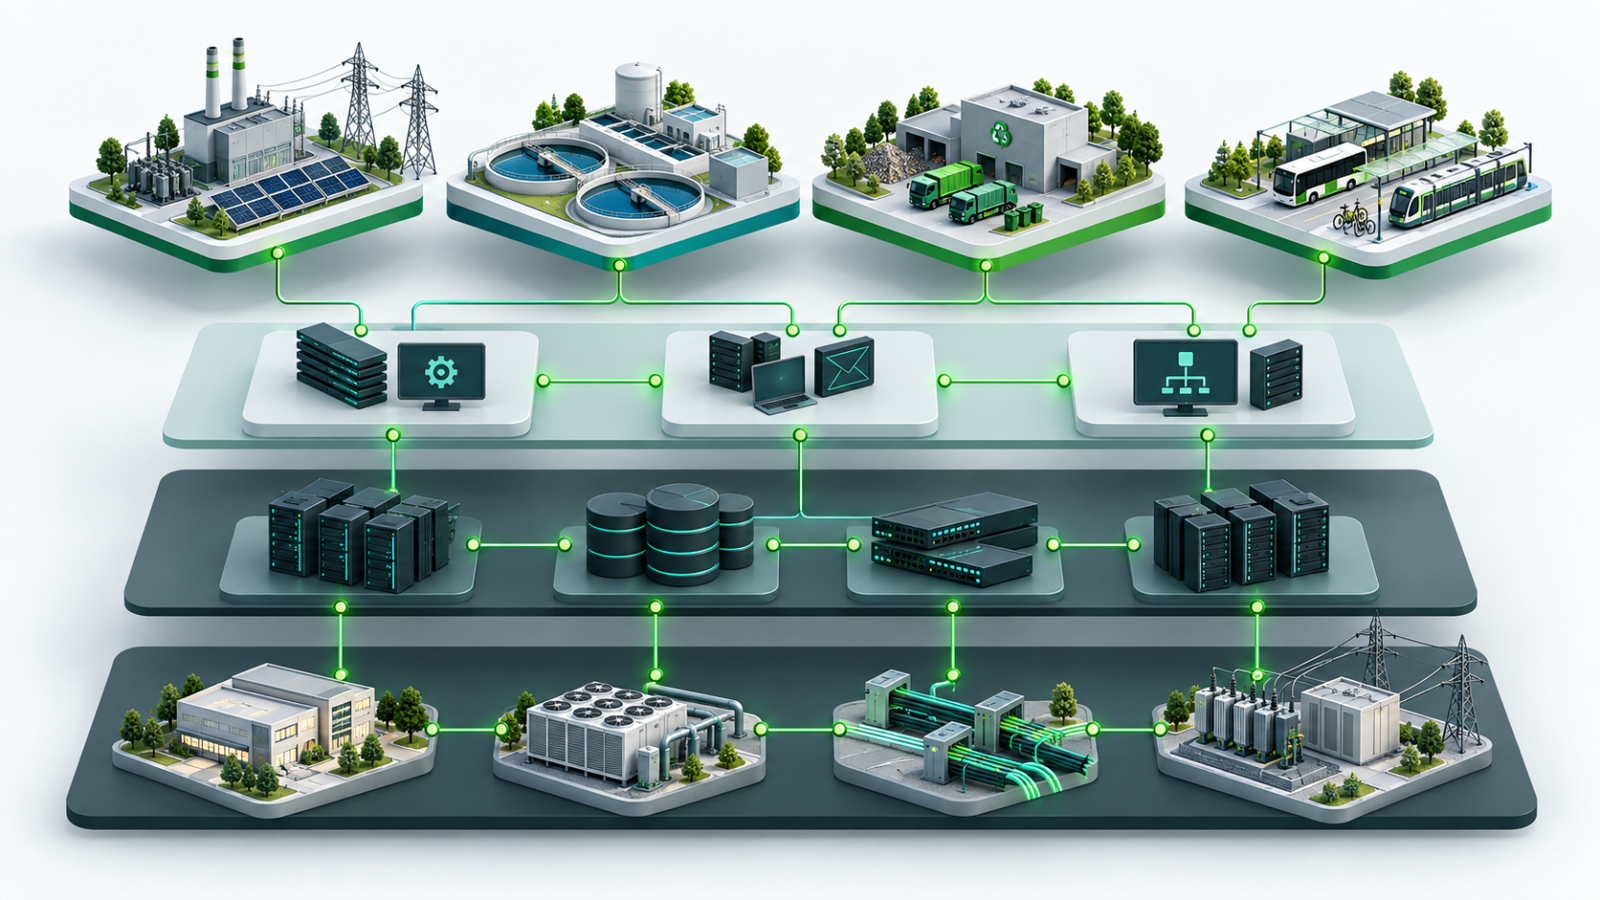
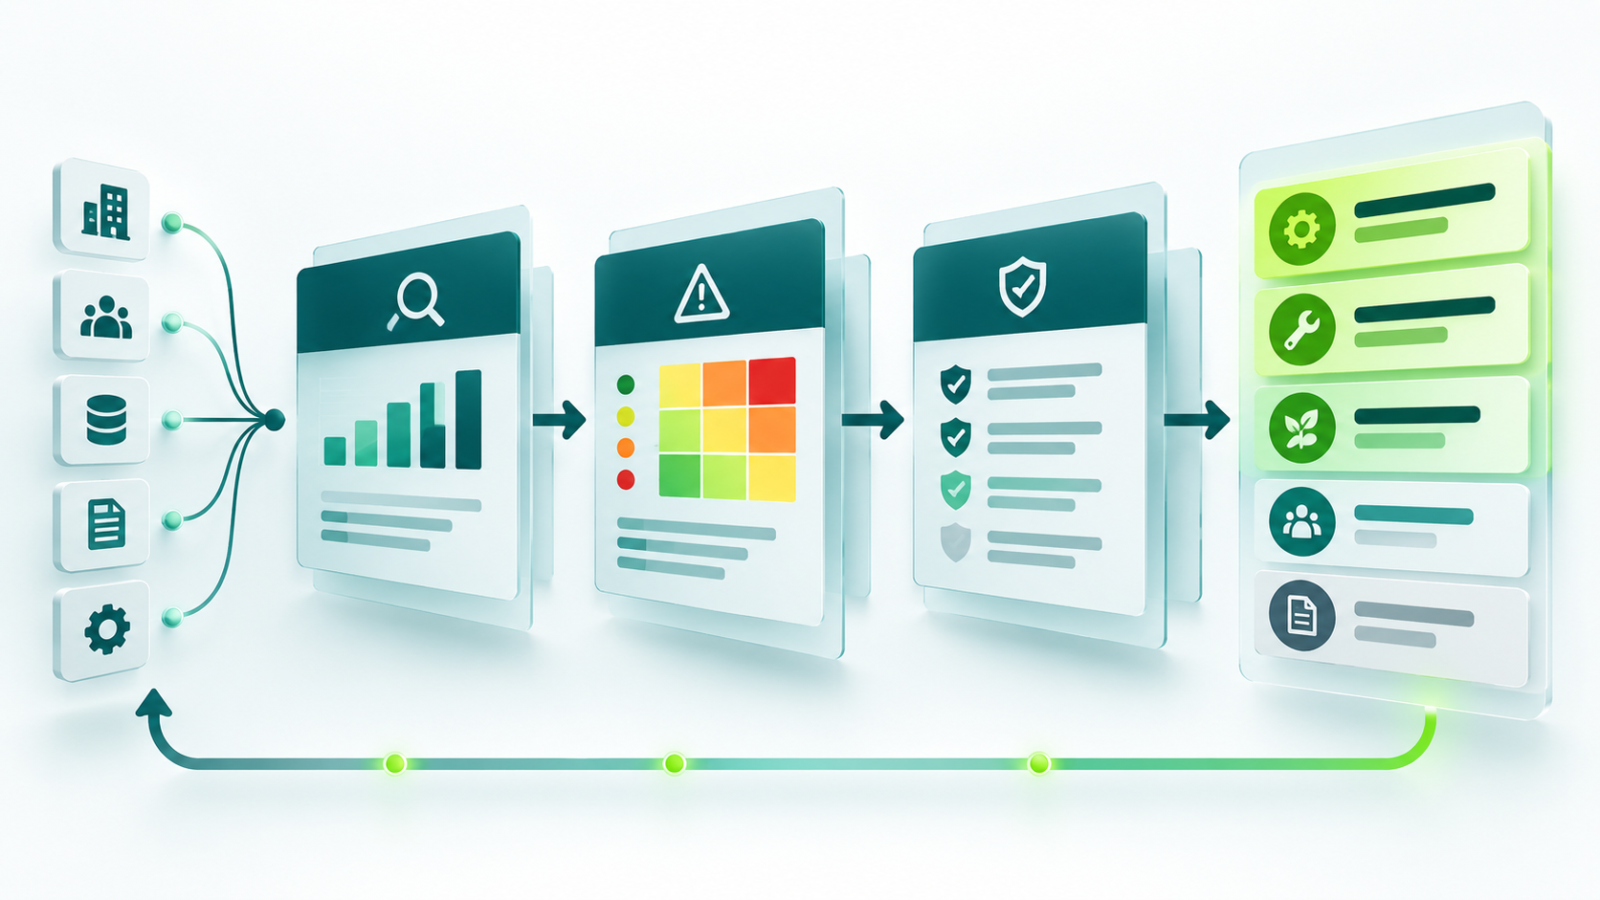
Implementation begins with modelling. Organisational units, services, processes, systems and technical resources are captured within a shared structure, creating a transparent view of their interdependencies. Before risks are assessed, organisations can identify which IT and infrastructure components support a critical service and where failures could have an impact across multiple areas.
The approach combines both top-down and bottom-up perspectives. At the level of critical services, protection requirements and potential impacts are assessed. At the level of core services and infrastructure, the likelihood of occurrence is evaluated. Linking these perspectives creates a robust foundation for the subsequent business impact analysis and risk analysis.
As part of the business impact analysis, Stadtwerke Bonn assesses the potential impact of disruptions. The risk analysis then adds the likelihood of these events occurring. Together, these assessments provide the basis for determining the overall level of risk. Because the underlying objects and dependencies have already been modelled, the assessment remains directly linked to the relevant causes and affected services.
The analysis is then used to define appropriate measures. These can be mapped to control objectives, consolidated and prioritised, making it clear which actions should be taken first and which risks they are designed to address. The presentation also highlighted a Monte Carlo simulation as a possible extension, with the results feeding into Enterprise Risk Management.
For regulated organisations, technical operability is just as important as the methodology itself. According to the presentation, CRISAM® is ISO 27001 multi-site certified, has achieved TISAX Assessment Level 3, and supports GDPR-compliant data processing. The platform can be deployed either as a SaaS solution or on premises. Single sign-on via Microsoft Entra ID or Active Directory, together with an open REST API, makes it easier to integrate CRISAM® into existing IT environments.
Cornelis Hilscher from the German Federal Network Agency provided another expert perspective. His presentation on IT and cybersecurity regulation reviewed current developments and outlined upcoming requirements. One message was clear: the more regulatory obligations organisations need to manage in parallel, the more important consistent processes, clearly defined responsibilities and auditable evidence become.
The Stadtwerke Bonn presentation showed how this works in practice. CRISAM® provides a shared foundation for modelling structures and dependencies, assessing business impacts and risks, and prioritising measures in a transparent and traceable way. This creates a consistent view that connects operational processes, information security and management reporting.
Organisations that still manage GRC, ISMS or BCM in separate tools should therefore take a closer look at their underlying data foundation. It determines whether information needs to be maintained multiple times or can be reused across different disciplines. CRISAM® supports this integrated approach through a modular platform that can be extended as requirements evolve.
Would you like to see how your existing GRC and ISMS landscape can be brought together on a single platform? In a personal CRISAM® live demo, we will show you how processes, risks, controls and evidence can be managed in an integrated way while building on and further developing your existing structures.
Schedule a personal CRISAM® live demo and discuss your current setup, requirements and next steps with our team.


You are currently viewing a placeholder content from Facebook. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More InformationYou need to load content from reCAPTCHA to submit the form. Please note that doing so will share data with third-party providers.
More InformationYou are currently viewing a placeholder content from Hubspot Embedded Content. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More InformationYou are currently viewing a placeholder content from HubSpot. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More InformationYou are currently viewing a placeholder content from Hubspot Meetings. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More InformationYou are currently viewing a placeholder content from Instagram. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More InformationYou are currently viewing a placeholder content from X. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More Information